
A Strategic Operating System and Board-Level Framework for Responsible AI Deployment.
- Executive Summary
- 1️⃣ The Core Problem: AI Scales Faster Than Policy
- 2️⃣ The 4-Layer AI Governance Architecture
- Layer 1: Strategic Governance (Board & Executive Level)
- Layer 2: Risk & Compliance Framework (Legal & IT Security)
- Layer 3: Operational Deployment Rules (Department Leads)
- Layer 4: Performance & ROI Measurement (Operations & Finance)
- 3️⃣ The Governance Control Matrix (Delegation Hierarchy)
- 4️⃣ Practical Implementation Framework: The 90-Day Rollout
- Phase 1: Audit & Discovery (Weeks 1–3)
- Phase 2: Policy Definition (Weeks 4–6)
- Phase 3: Tool Consolidation (Weeks 7–10)
- Phase 4: Training & Activation (Weeks 11–13)
- 5️⃣ The Enterprise AI Readiness Score
- 6️⃣ The Risks of Over-Governance
- 7️⃣ Best Practices Checklist
- FAQ
Executive Summary
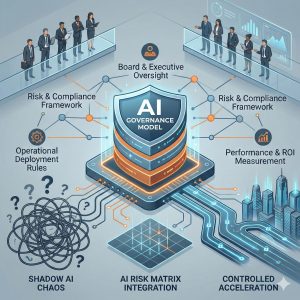
AI deployment without governance creates systemic risk. While marketing and operations teams rapidly adopt generative tools to accelerate workflows, organizations face mounting exposure to data leakage, copyright infringement, and regulatory non-compliance. This uncoordinated adoption is known as Shadow AI.
The AI Governance Model is a strategic operating system that defines decision authority, risk classification, and oversight protocols. It shifts the organizational posture from reactive restriction to controlled acceleration.
This framework introduces a 4-Layer Governance Architecture, an actionable 90-day rollout plan, and a measurable AI Readiness Score to help executives scale AI safely.
Methodology Note:
This governance model relies on the foundational AI Risk Matrix (2×2 Model) to classify tasks and determine appropriate “Human-in-the-Loop” requirements.
1️⃣ The Core Problem: AI Scales Faster Than Policy
AI tools are inherently viral. Adoption typically happens bottom-up:
- Marketing experiments with copy generation.
- Developers integrate coding copilots.
- Finance automates spreadsheet reporting.
Meanwhile, the protective layers of the business lag behind. Legal has no policy, IT lacks audit trails, and Security has no visibility into what proprietary data is being pasted into public LLMs.
The result is uncoordinated automation. Governance must precede scale.
2️⃣ The 4-Layer AI Governance Architecture
Effective AI governance operates across four structural layers, bridging the gap between the Boardroom and the daily workflow.
Layer 1: Strategic Governance (Board & Executive Level)
Defines the organization’s AI risk appetite and fiduciary limits.
- Key Questions: What decisions must remain human-only? What is our tolerance for AI error? Where does liability transfer occur?
- Deliverables: AI Governance Charter, Enterprise Risk Matrix adoption.
Layer 2: Risk & Compliance Framework (Legal & IT Security)
Ensures regulatory alignment and data protection.
- Key Controls: Vendor AI due diligence, Data Sanitization policies (PII/IP protection), Audit logging, and industry compliance (HIPAA, GDPR, SOC2).
Layer 3: Operational Deployment Rules (Department Leads)
Defines how AI is used day-to-day.
- Key Controls: Mandating when Human-in-the-Loop (HITL) is required, setting Red Team simulation requirements, and establishing prompt engineering SOPs.
Layer 4: Performance & ROI Measurement (Operations & Finance)
Governance without measurement is just bureaucracy.
- Key Metrics: Hours saved vs. Verification Tax (time spent reviewing AI output), error reduction rates, and employee adoption velocity.
3️⃣ The Governance Control Matrix (Delegation Hierarchy)
To operationalize governance, ambiguity in approval chains must be eliminated. Every AI deployment must be classified using the AI Risk Matrix and mapped to a specific approval authority.
| Risk Matrix Zone | Governance Action | Approval Authority | Audit Frequency |
|---|---|---|---|
| 🟢 Safe Zone | Fully Delegate. Standard tools approved for daily use. | Operational Staff | Annual |
| 🟡 Draft Zone | Iterate. Approved for ideation; data upload rules apply. | Department Lead | Bi-Annual |
| 🔴 Review Zone | Trust but Verify. Mandatory HITL protocols enforced. | Compliance / Legal | Quarterly |
| ⛔ Fiduciary Boundary | Prohibit Automation. Human decision required. | Executive / Board | Continuous |
Granularity prevents systemic risk. Do not approve “AI for Legal”; approve “Clause Extraction (Review Zone)” and prohibit “Litigation Strategy (Boundary).”
4️⃣ Practical Implementation Framework: The 90-Day Rollout
Moving from zero governance to structured control requires a phased approach.
Phase 1: Audit & Discovery (Weeks 1–3)
- Actions: Map all current AI usage. Identify Shadow AI via network logs. Classify discovered workflows using the AI Risk Matrix.
- Deliverable: Enterprise AI Exposure Map.
Phase 2: Policy Definition (Weeks 4–6)
- Actions: Draft the AI Acceptable Use Policy (AUP). Define “Red Line” data that can never be uploaded. Establish the approval hierarchy.
- Deliverable: AI Governance Charter.
Phase 3: Tool Consolidation (Weeks 7–10)
- Actions: Procure and approve enterprise-grade AI tools (with zero-data-retention agreements). Block unauthorized integrations at the firewall level. Set up audit logging.
- Deliverable: Secured AI Environment.
Phase 4: Training & Activation (Weeks 11–13)
- Actions: Train teams on the Risk Matrix. Simulate failure scenarios (AI Red Teaming).
- Deliverable: Operational Governance Activation.
5️⃣ The Enterprise AI Readiness Score
Evaluate your organization across these six pillars. Score each from 1 (Non-existent) to 5 (Fully Optimized):
| Governance Pillar | Score (1–5) |
|---|---|
| 1. Defined AI Acceptable Use Policy (AUP) | |
| 2. Strict Data Classification & Upload Rules | |
| 3. AI Risk Matrix Embedded in SOPs | |
| 4. Standardized Vendor Review Process | |
| 5. Active Audit Logging & Shadow AI Monitoring | |
| 6. Executive-Level Oversight Committee | |
| Total Score: | / 30 |
- 0–10: High Exposure Risk (Immediate action required).
- 11–20: Partial Governance (Vulnerable to edge cases).
- 21–30: Structured Control (Ready to scale).
6️⃣ The Risks of Over-Governance
Too much restriction is as dangerous as too little. Over-governance causes employee resistance, innovation slowdown, and a resurgence of Shadow AI (employees using personal devices to bypass corporate blocks).
Governance must balance Control vs. Enablement. The goal is structured acceleration, not bureaucratic paralysis.
7️⃣ Best Practices Checklist
- ✔ DO define an AI Governance Charter.
- ✔ DO embed the AI Risk Matrix into daily SOPs.
- ✔ DO implement network-level audit logging.
- ✘ DO NOT centralize AI tools without offering transparent, sanctioned alternatives.
- ✘ DO NOT allow the automation of high-exposure analytical decisions (Fiduciary Boundary).
FAQ
What is AI Governance?
AI Governance is the structured system of policies, oversight, and accountability that regulates how AI tools are deployed, ensuring alignment with legal, ethical, and business standards.
Who should own AI governance?
Strategic oversight belongs to the Executive Board or a dedicated AI Steering Committee. Operational enforcement belongs to Compliance, IT, and Department Heads.
Is AI governance required by law?
In regulated industries (finance, healthcare, defense), governance is effectively mandatory due to existing compliance obligations (e.g., HIPAA, GDPR). Furthermore, upcoming frameworks like the EU AI Act will make governance legally binding for many systems.
Does governance slow innovation?
If designed properly, governance accelerates safe adoption by clarifying boundaries. Employees innovate faster when they know exactly where the guardrails are.
Last updated: 2026